DeepSeek Harness (DSH) Automation Safety: Security, Permission & Cost Plugins
TL;DRDeepSeek Harness (DSH) plugins run with your permissions, so an unattended run can delete a file, leak a key or burn through your token budget. Scan plugins before install, keep a recycle-bin guard and a secret scanner on, review the output with a second model, and set a monthly budget. The official notice says DSH has not had a security audit, so keep backups.
By Cameron Voss
On this page
- What can go wrong on an unattended run?
- Layer 1: how do you check a plugin before installing it?
- Layer 2: how do you stop a bad delete or a leaked key?
- Layer 3: how do you make the agent check its own work?
- How do you keep token spend under control?
- What does least privilege look like in practice?
- What should you check before the first unattended run?
- What can these guardrails not do?
- FAQ
DeepSeek Harness (DSH) is DeepSeek's open-source agent harness. Its design is "everything is a plugin", and a plugin runs as third-party code with your permissions. Tool approvals do not sandbox plugin code. The community plugin list says so, and the project's safety notice says DSH has not had a security audit.
What can go wrong on an unattended run?
Three failures cover most of the damage. A cleanup task builds the wrong path and runs a recursive delete. A key in a config file gets read by a plugin or committed by the agent. A retry loop or a subagent fan-out multiplies calls until the bill is much larger than planned. Nothing looks broken in the chat window.
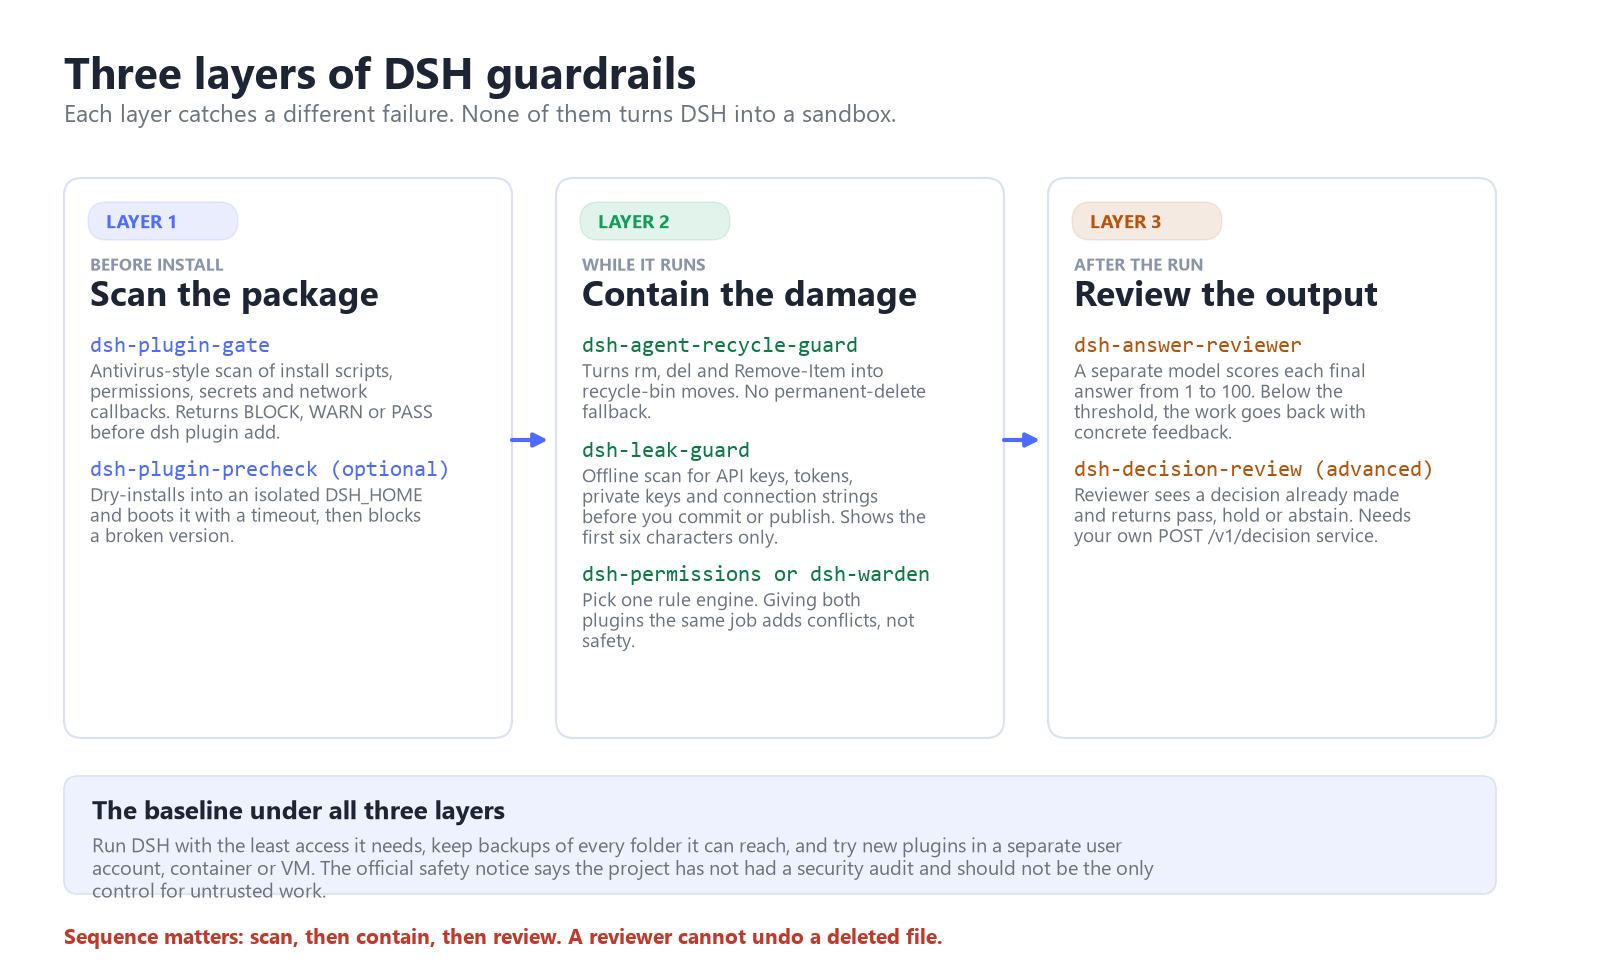
Layer 1: how do you check a plugin before installing it?
dsh-plugin-gate scans a local directory or npm tarball for risky install scripts, permissions, secrets and network callbacks, then returns BLOCK, WARN or PASS before dsh plugin add. The point is to make you look at the package before it runs.
dsh-plugin-precheck covers compatibility instead: it dry-installs into an isolated DSH_HOME and boots with a timeout, so a plugin that cannot run on your DSH version never reaches your real profile. Neither tool replaces reading the source. Inclusion in the plugin list is not a security review.
Layer 2: how do you stop a bad delete or a leaked key?
dsh-agent-recycle-guard rewrites delete commands into recycle-bin operations. It covers PowerShell Remove-Item, Bash rm, unlink, rmdir, and CMD del, erase, rd, and it keeps no permanent-delete fallback. The bin can still be emptied, so it is not a backup.
dsh-leak-guard walks a directory and flags API keys, tokens, private keys, connection strings and hard-coded passwords before you commit or publish. It runs offline, has zero dependencies, and shows only the first six characters of a match.
For permissions, pick one engine. dsh-permissions gives you hard, deny, ask and allow tiers with workspace rules; dsh-warden uses a local regex pass and only calls a review model on a hit. Running both adds conflicts without adding safety. CC Safety Net is a separate command-level net: it blocks destructive commands and secret access before they run, and it is not a sandbox.
The rule that matters most: give the agent the project folder, not your home directory.
Layer 3: how do you make the agent check its own work?
dsh-answer-reviewer sends each final answer to a second model for a 1-100 score. Below your threshold, the work goes back with concrete feedback. That catches the confident answer that skipped a requirement, which is the usual failure on a long run.
dsh-decision-review is optional and more involved: it reviews a decision the main model already made and needs your own POST /v1/decision service. If you cannot run that service, leave it off. This layer checks output quality, not file safety.
How do you keep token spend under control?
Measure, cap, shift and audit.
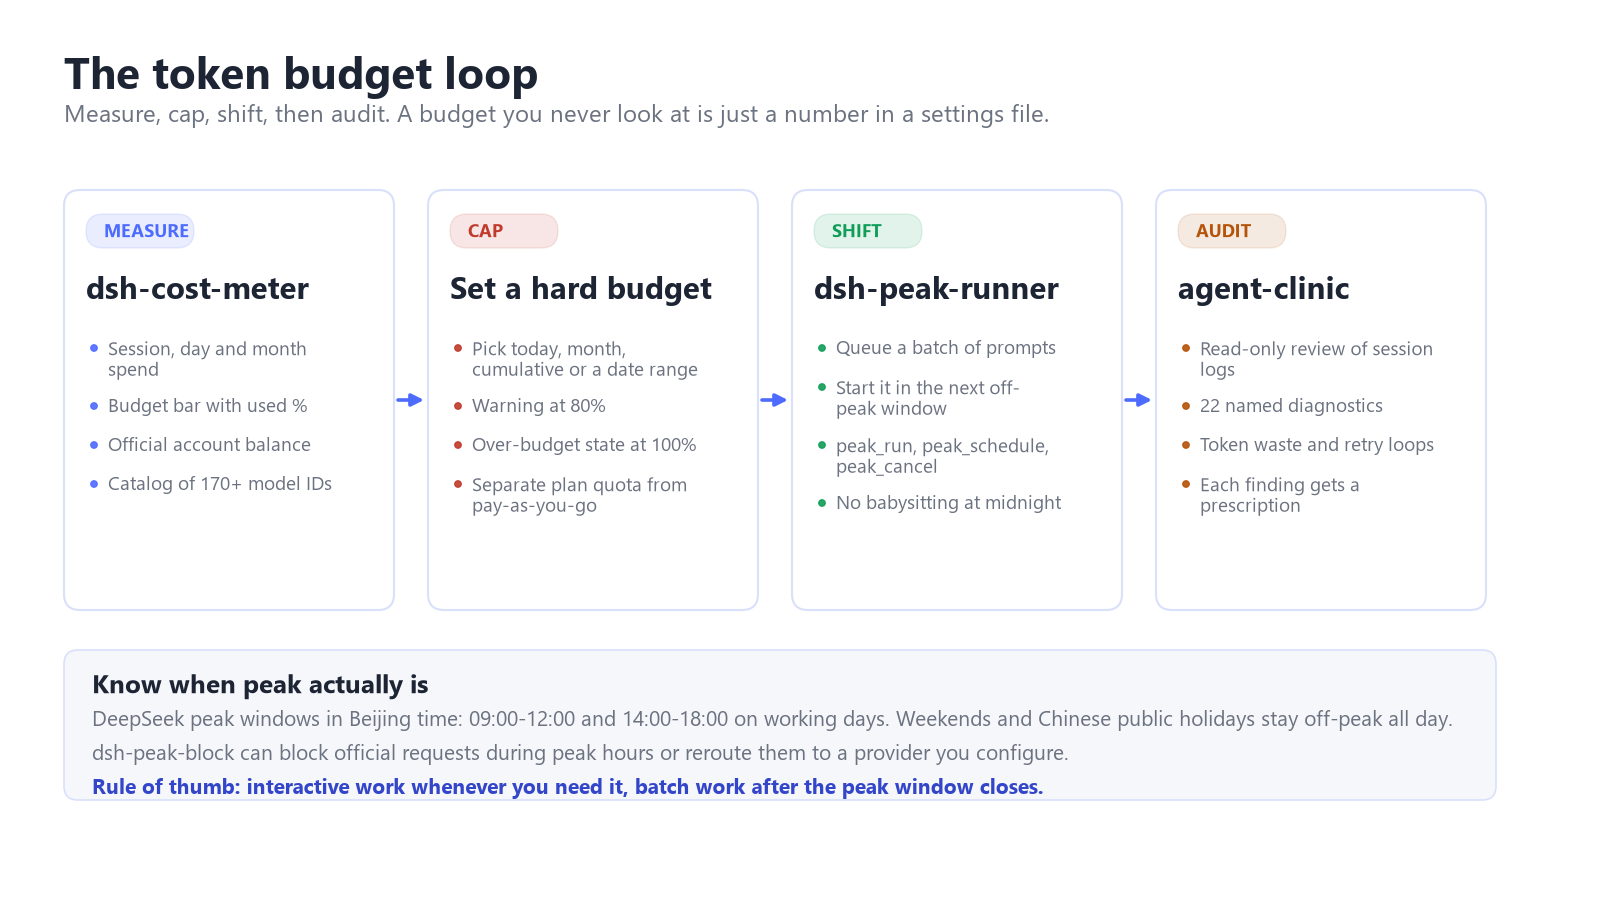
dsh-cost-meter shows session, daily and monthly cost, the official balance, plan versus pay-as-you-go spend, and prices against a 170+ model catalog. Set a monthly budget with an 80 percent warning. A meter can show you are over budget without stopping the run, so also set a provider-side spend cap.
dsh-peak-runner queues batch work and starts it in the next off-peak window, using peak_run, peak_schedule and peak_cancel. DeepSeek peak hours are 09:00-12:00 and 14:00-18:00 Beijing time on working days; weekends and public holidays are off-peak. dsh-peak-block blocks or reroutes peak requests instead.
After the first week, run agent-clinic. It reads session logs and names 22 kinds of waste, each with a prescription. For teams, dsh-team-cost adds member budgets and 80/100 percent alerts.
What does least privilege look like in practice?
- Run DSH as a separate user, in a container or in a VM.
- Mount one project folder. Keep the home directory and SSH folder out.
- Use a low-limit API key for automation, and rotate it if a scan finds it.
- Allow reads, ask for writes, deny deletes outside the project.
Keep backups of every folder DSH can reach. The safety notice recommends this, and a recycle bin does not cover a wiped disk or an in-place overwrite.
What should you check before the first unattended run?
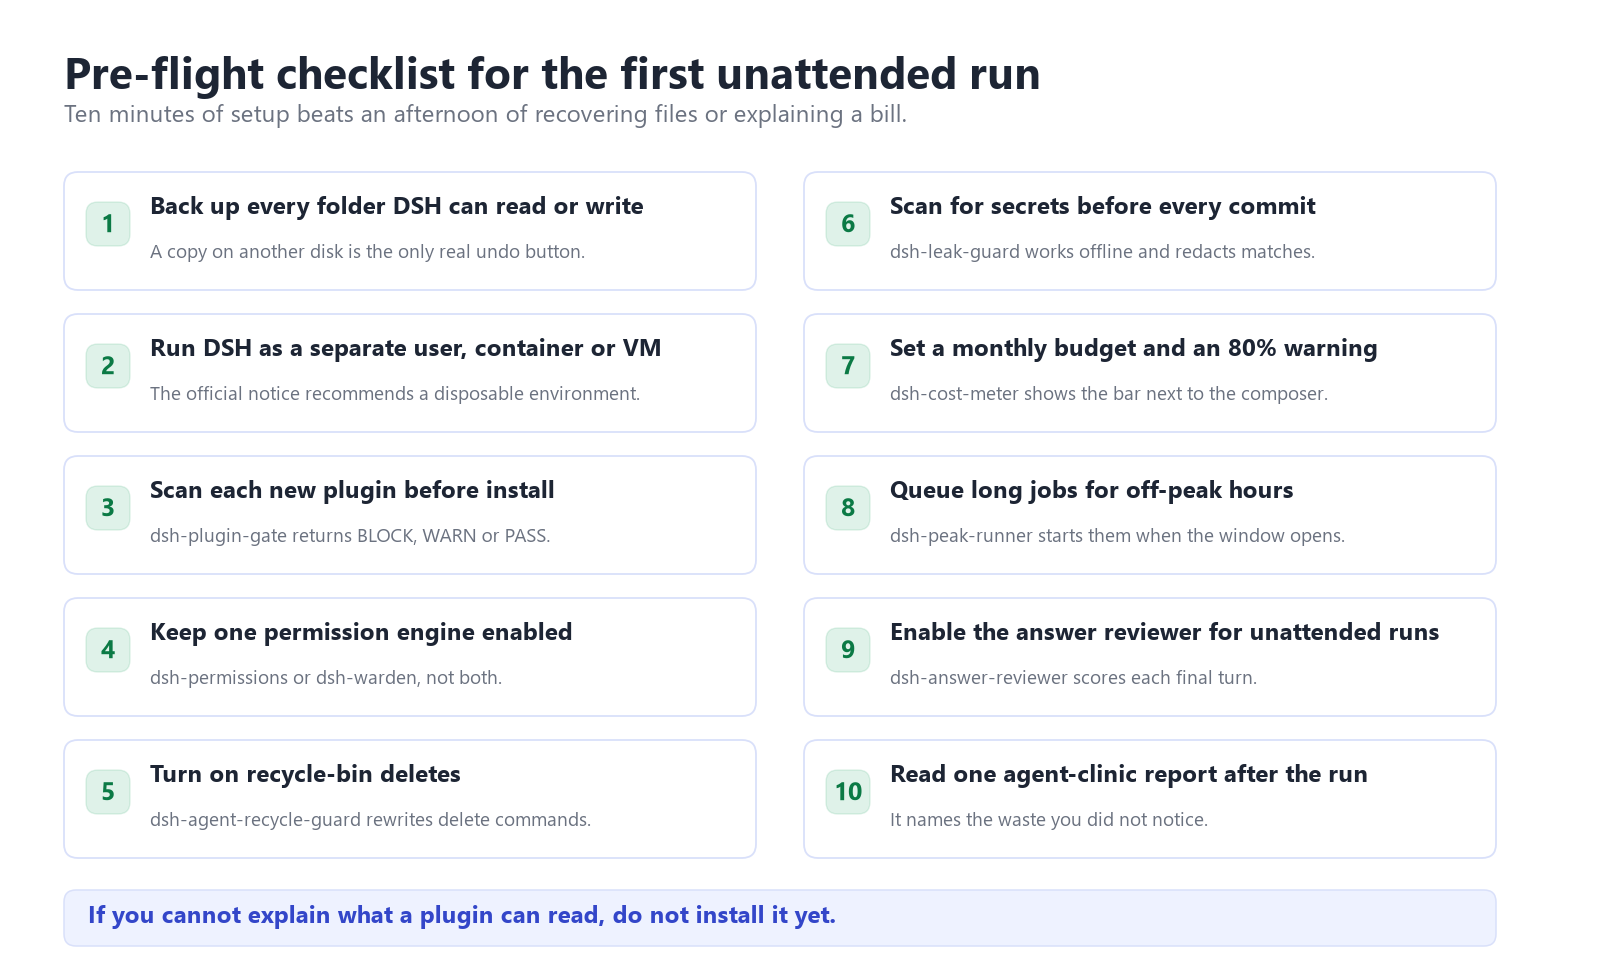
If you do only four things, do these: back up the folder, scan the plugin, turn on recycle-bin deletes, and set a budget. They cover the two fears that stop most people from trying automation.
What can these guardrails not do?
- A plugin still runs with your permissions, and approvals do not cover its code.
- A recycle bin is not a backup.
- A budget bar may not stop a run that is already going.
- A review model can share the main model's blind spot.
The official notice is explicit: DSH is developer-preview software, it has not had a security audit, and sandboxing cannot protect resources it is allowed to access. Do not make it the only control for untrusted work.
FAQ
Do I need all of these plugins?
No. The minimum is a backup, a plugin scan, a recycle-bin delete guard and a budget. Add the secret scanner if the workspace has keys, and the reviewer for unattended runs.
How do I set a token limit in DSH?
In dsh-cost-meter, set a monthly budget and an 80 percent warning. Confirm whether it enforces or only displays the limit, then add a provider-side cap.
Are these guardrail plugins official DeepSeek plugins?
Most are community plugins. The list checks that they install, not that they are safe. DSH itself is official developer-preview software without a security audit.